
Overview
Health and care providers carry a combination attackers find worthwhile: sensitive personal data, clinical systems that cannot easily be taken offline, and a long supplier chain. Assessment work in this sector has to account for all three, and for the assurance evidence that commissioners and the Data Security and Protection Toolkit ask for.
We recognise that balancing rapid digital innovation with strict NHS requirements feels like a moving target. This guide covers the technical assurance work involved, and how to check which DSPT category and cycle applies to you before scoping anything. We’ll examine how to transition from point-in-time testing to a model of continuous resilience, ensuring your infrastructure remains secure against both state-sponsored threats and identity-based attacks.
Navigating the UK Healthcare Data Security Landscape in 2026
A healthcare data security assessment uk is a comprehensive evaluation of the technical and administrative controls designed to protect patient information. In 2026, this process has evolved from a simple compliance exercise into a critical pillar of clinical safety. It’s no longer sufficient to claim security; organisations must demonstrate it through rigorous evidence and technical assurance. Effective assessments bridge the gap between high-level policy and the practical reality of defending complex clinical networks.
Handling “special category data” under the Data Protection Act 2018 and UK GDPR requires a strategic approach to risk management. This data, which includes health records and genetic information, carries the highest level of sensitivity. Assurance in this sector has been moving away from pure self-declaration towards independent validation for higher-risk organisations.
The Role of the Data Security and Protection Toolkit (DSPT)
The DSPT remains the non-negotiable foundation for any organisation seeking access to NHS patient data and systems. It’s structured around the 10 Data Security Standards defined by the National Data Guardian, which cover leadership, training, and technical defences. While self-assessment is the starting point, the 2025-2026 cycle for Version 8 emphasizes audited evidence. There’s a clear distinction between a “tick-box” submission and a technically validated one. We provide the human-led testing required to turn a standard submission into a robust statement of technical assurance, so the evidence is in place before your DSPT submission is due.
Beyond GDPR: Specific Healthcare Regulations
Compliance in the UK health sector extends into specialized frameworks that go beyond general data protection rules. The UK Medical Device Regulations (UK MDR 2002) now impose strict security requirements on Software as a Medical Device (SaMD), ensuring that code vulnerabilities don’t translate into clinical risks. Furthermore, the Digital Technology Assessment Criteria (DTAC) serves as the benchmark for health tech procurement, focusing on clinical safety and data confidentiality. Every assessment must also incorporate the Caldicott Principles. These principles ensure that every instance of data access is necessary, proportionate, and governed by a culture of trust and transparency.
The Components of a Robust Healthcare Data Security Assessment
A modern healthcare data security assessment uk must account for the diverse technical layers within a Trust or private healthcare provider. It is no longer enough to test the perimeter. You must validate the security of internal clinical networks, public-facing patient portals, and the cloud-hosted databases that store sensitive records. This modular approach ensures that a failure in one area, such as a misconfigured IoT device, doesn’t lead to a total compromise of the patient record system. We focus on identifying these interconnected risks to provide a clear picture of your actual defensive posture.
The assessment process includes infrastructure penetration testing to secure the backbone of clinical networks, alongside web application testing for patient portals. As more organisations migrate to AWS, Azure, or GCP, cloud security assessments become vital for evaluating configurations against NHS data offshoring standards. We also address the growing attack surface of mobile apps and wearable medical devices. These remote monitoring tools often lack the rigorous security controls found in centralized systems, making them attractive targets for adversary simulation.
Securing Patient Portals and Web Applications
Patient portals serve as the primary interface for data access, making them high-value targets. We frequently identify critical vulnerabilities like Insecure Direct Object References (IDOR) and broken access control that automated tools miss. These flaws could allow an unauthorised user to view the medical history of another patient simply by modifying a URL parameter. Testing must also extend to the API endpoints that facilitate data exchange between providers. Human-led testing is essential here; our experts simulate complex clinical workflows to uncover logic flaws that could lead to unauthorised data exfiltration. If you need to validate your external defences, our team provides tailored web application penetration testing to ensure your portals remain resilient.
Cloud and Infrastructure Resilience
Transitioning to the cloud offers scalability, but it also introduces the risk of misconfigured storage buckets or overly permissive IAM roles. These errors are a leading cause of data exposure. A thorough assessment evaluates these configurations against the standards set by the Data Security and Protection Toolkit. We use infrastructure penetration testing to identify lateral movement risks. This is particularly vital when securing legacy clinical systems that weren’t designed for modern internet connectivity. Attackers often exploit these older systems as an entry point to move toward secure cloud environments. By identifying these paths early, we provide the remediation guidance necessary to harden your infrastructure and maintain long-term assurance.
DSPT Self-Assessment vs. Independent Technical Validation
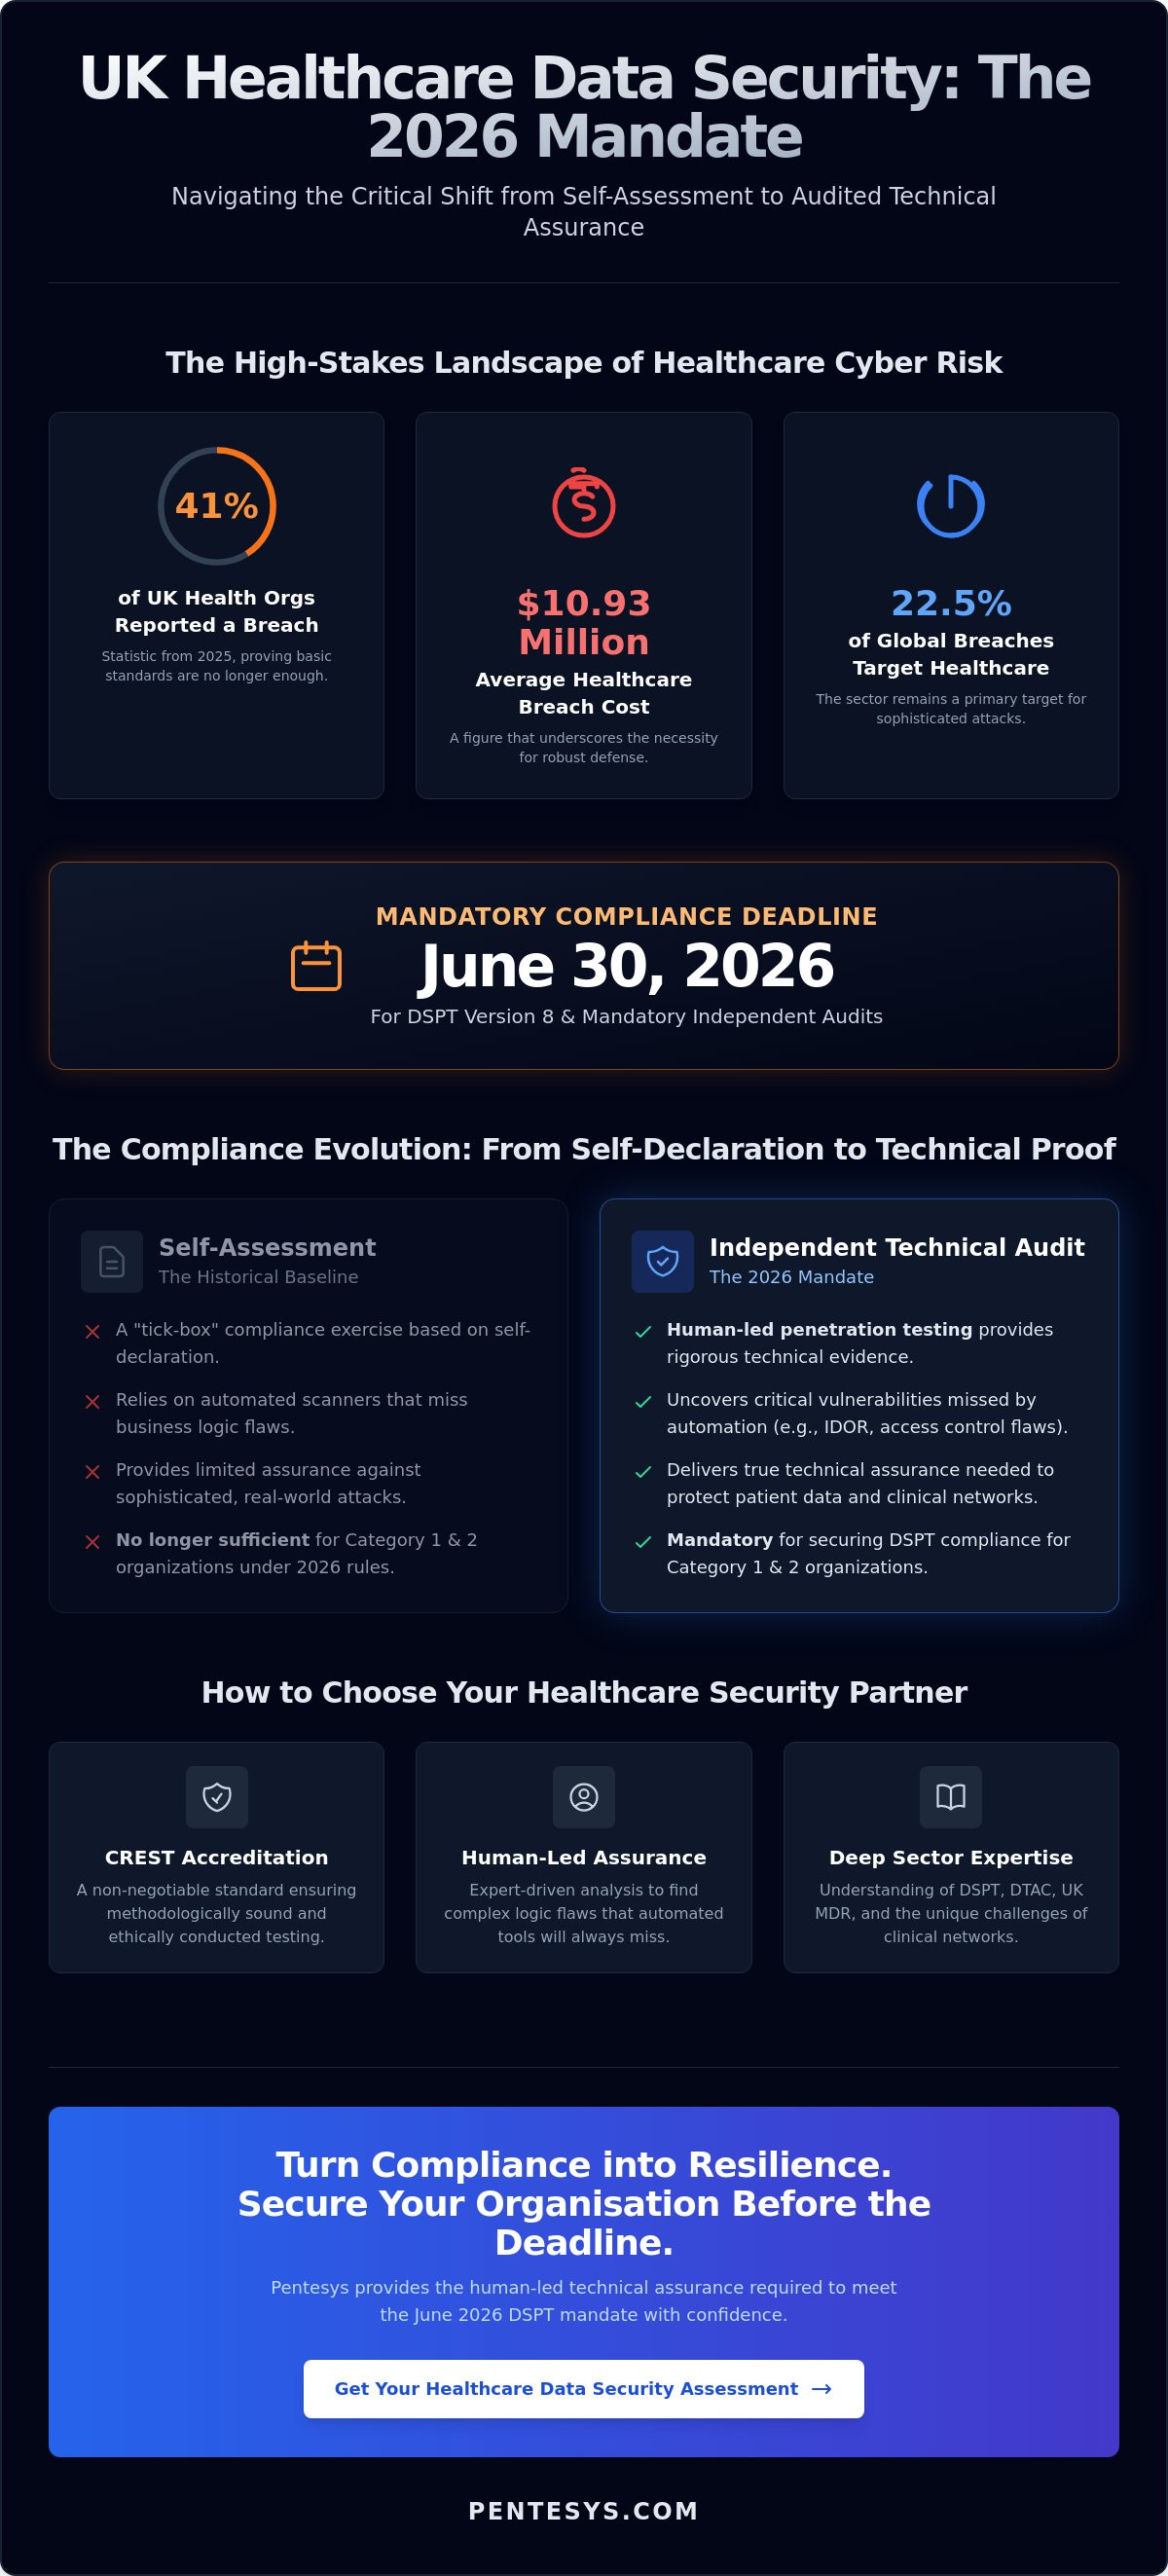
Passing the DSPT is a contractual requirement, but it isn’t a guarantee of technical resilience. While the toolkit provides a necessary administrative framework, it often functions as a “tick-box” exercise that documents the existence of policies rather than their actual effectiveness. A healthcare data security assessment uk must bridge this gap by adopting a “prove it” mentality. Relying solely on self-assessment creates a dangerous disconnect between perceived security and operational reality. Technical validation through penetration testing provides the definitive evidence of effectiveness required to satisfy both internal stakeholders and external regulators.
Boards often ask why they need independent testing after passing the DSPT. The answer lies in the distinction between compliance and security. Compliance is the baseline; technical assurance is the validation of that baseline in the face of an active adversary. Automated vulnerability scans often contribute to a sense of false confidence by flagging known software flaws while missing the complex logic errors and lateral movement paths that human experts identify.
Why Self-Assessment is No Longer Sufficient
The rise in sophisticated ransomware targeting UK providers has made administrative audits insufficient. These attacks frequently exploit identity misuse and compromised credentials, which are the root cause of most breaches. Adversarial simulations reveal the technical blind spots that a paperwork check will never surface. For instance, testing the “Human Element” through social engineering is critical in clinical settings where staff are under high pressure. We simulate these real-world scenarios to ensure your team can recognise and respond to phishing attempts before they escalate into full-scale data corruption events.
The Value of Independent Technical Assurance
Assurance represents the measurable confidence that your security controls will perform as expected when under attack. This is a central theme in the NCSC Board Toolkit, which encourages leaders to seek objective evidence of their organisation’s cyber health. Utilising CREST accredited penetration testing provides the external credibility needed for successful NHS contract procurement. This level of technical scrutiny is the hallmark of a high-quality healthcare data security assessment uk. Beyond the initial test, we deliver a detailed remediation roadmap through the Pentesys Portal. This structured approach allows your technical teams to move from being merely “compliant” to truly secure, focusing on actionable insights rather than temporary fixes.
How to Choose a Healthcare Security Assessment Provider
Selecting a partner for a healthcare data security assessment uk requires moving beyond basic procurement toward a model of strategic alignment. Clinical environments present unique technical hurdles that a generic testing approach will likely overlook. You need a provider that understands the operational pressures of a Trust while maintaining the technical authority to navigate evolving regulations. Pentesys Limited acts as this sophisticated ally; we provide the expertise required to build long-term resilience rather than just meeting immediate audit requirements.
A high-quality provider must offer a methodology that integrates human intuition with advanced technical execution. This ensures the assessment covers the entire ecosystem, including the identity-based attack vectors that are becoming increasingly prevalent. Your choice should depend on a provider’s ability to deliver actionable insights that bridge the gap between deep-tech execution and business value. This moves the conversation from simple vulnerability counts to strategic risk management.
Critical Accreditation and Expert Markers
CREST accreditation is the non-negotiable benchmark for any UK provider. It guarantees that the individuals performing your assessment adhere to strict ethical codes and have passed rigorous technical examinations. For organisations handling sensitive patient records, SC-cleared testers provide an additional layer of assurance. We prioritise human-led testing because automated tools cannot replicate the creative problem-solving of a skilled adversary. If you’re ready to move beyond automated checklists, you can book a professional security assessment with Pentesys Limited to validate your defences.
Continuous Monitoring for the Digital Health Estate
The transition from point-in-time testing to continuous security validation is essential for modern HealthTech firms. As your digital estate grows, so does your attack surface. Pentesys Limited provides continuous external attack surface monitoring to identify new risks as they emerge, bridging the gap between deep-tech execution and executive business value. This proactive stance moves your organisation beyond reactive fixes toward long-term resilience. It’s a structured rhythm of security that mirrors the continuous nature of the healthcare services you provide. Secure your healthcare data with Pentesys Limited expert-led assessments.
Is a penetration test mandatory for NHS DSPT compliance?
Requirements vary by DSPT category and cycle, so confirm your organisation's category and the current cycle directly rather than relying on a general answer. While smaller entities may rely on self-assessment, high-risk processors must provide evidence of effectiveness through professional testing. This validation is essential for maintaining access to NHS systems and demonstrating a commitment to protecting special category data.
How does the DTAC impact security assessments for health apps?
The Digital Technology Assessment Criteria (DTAC) sets the benchmark for clinical safety and data confidentiality for health technologies. It requires evidence of rigorous security testing, specifically focusing on API and mobile application assessments. Meeting DTAC standards is essential for any developer seeking to have their technology adopted by NHS Trusts or social care providers in 2026.
Can a security assessment be performed on live clinical systems without downtime?
Yes, professional testers perform assessments on live systems by using non-disruptive methodologies. We coordinate with your technical teams to establish clear rules of engagement before testing begins. This ensures that infrastructure and application testing occur safely without impacting critical patient care or clinical workflows, allowing you to maintain operational continuity throughout the process.
Founder & CEO, Pentesys
James Hinton is the founder of Pentesys, a CREST-approved UK company working only on offensive security: penetration testing, PTaaS, CTEM, external attack surface management and red teaming. He built the business around one discipline rather than a broad consultancy menu, and most of his time still goes on how engagements get scoped, delivered and reported. He writes here about the practical side of security testing and what buyers should be asking for.
LinkedIn profile