
Your last pentest is already out of date
You ship weekly, but you test once a year. Everything released since that report is untested and unproven.
CREST-approved penetration testing, red teaming and continuous exposure validation — combining expert human testing with AI-assisted security assessment.
Accredited and independently assessed
 CREST Approved
 CREST AI Charter
 Cyber Essentials
“Pentesys has continuously produced excellent work. Their group demonstrated extraordinary technical proficiency by spotting crucial flaws and offering clever fixes that greatly strengthened our security stance.”
Most teams don't have a testing problem — they have a visibility, validation and follow-through problem.
You ship weekly, but you test once a year. Everything released since that report is untested and unproven.
Forgotten subdomains, shadow cloud assets and exposed services appear faster than anyone can inventory them.
A 90-page report lands in an inbox. Nobody owns the remediation and nothing gets validated as fixed.
Customers, auditors and insurers want evidence now — and procurement stalls until you can produce it.
Pentesys combines attack-surface visibility, expert security testing, remediation workflows and assurance within a single continuous security model.
Map every internet-facing asset and exposure.
Prove what is genuinely exploitable.
Route findings to owners with SLAs.
Retest and evidence the fix.
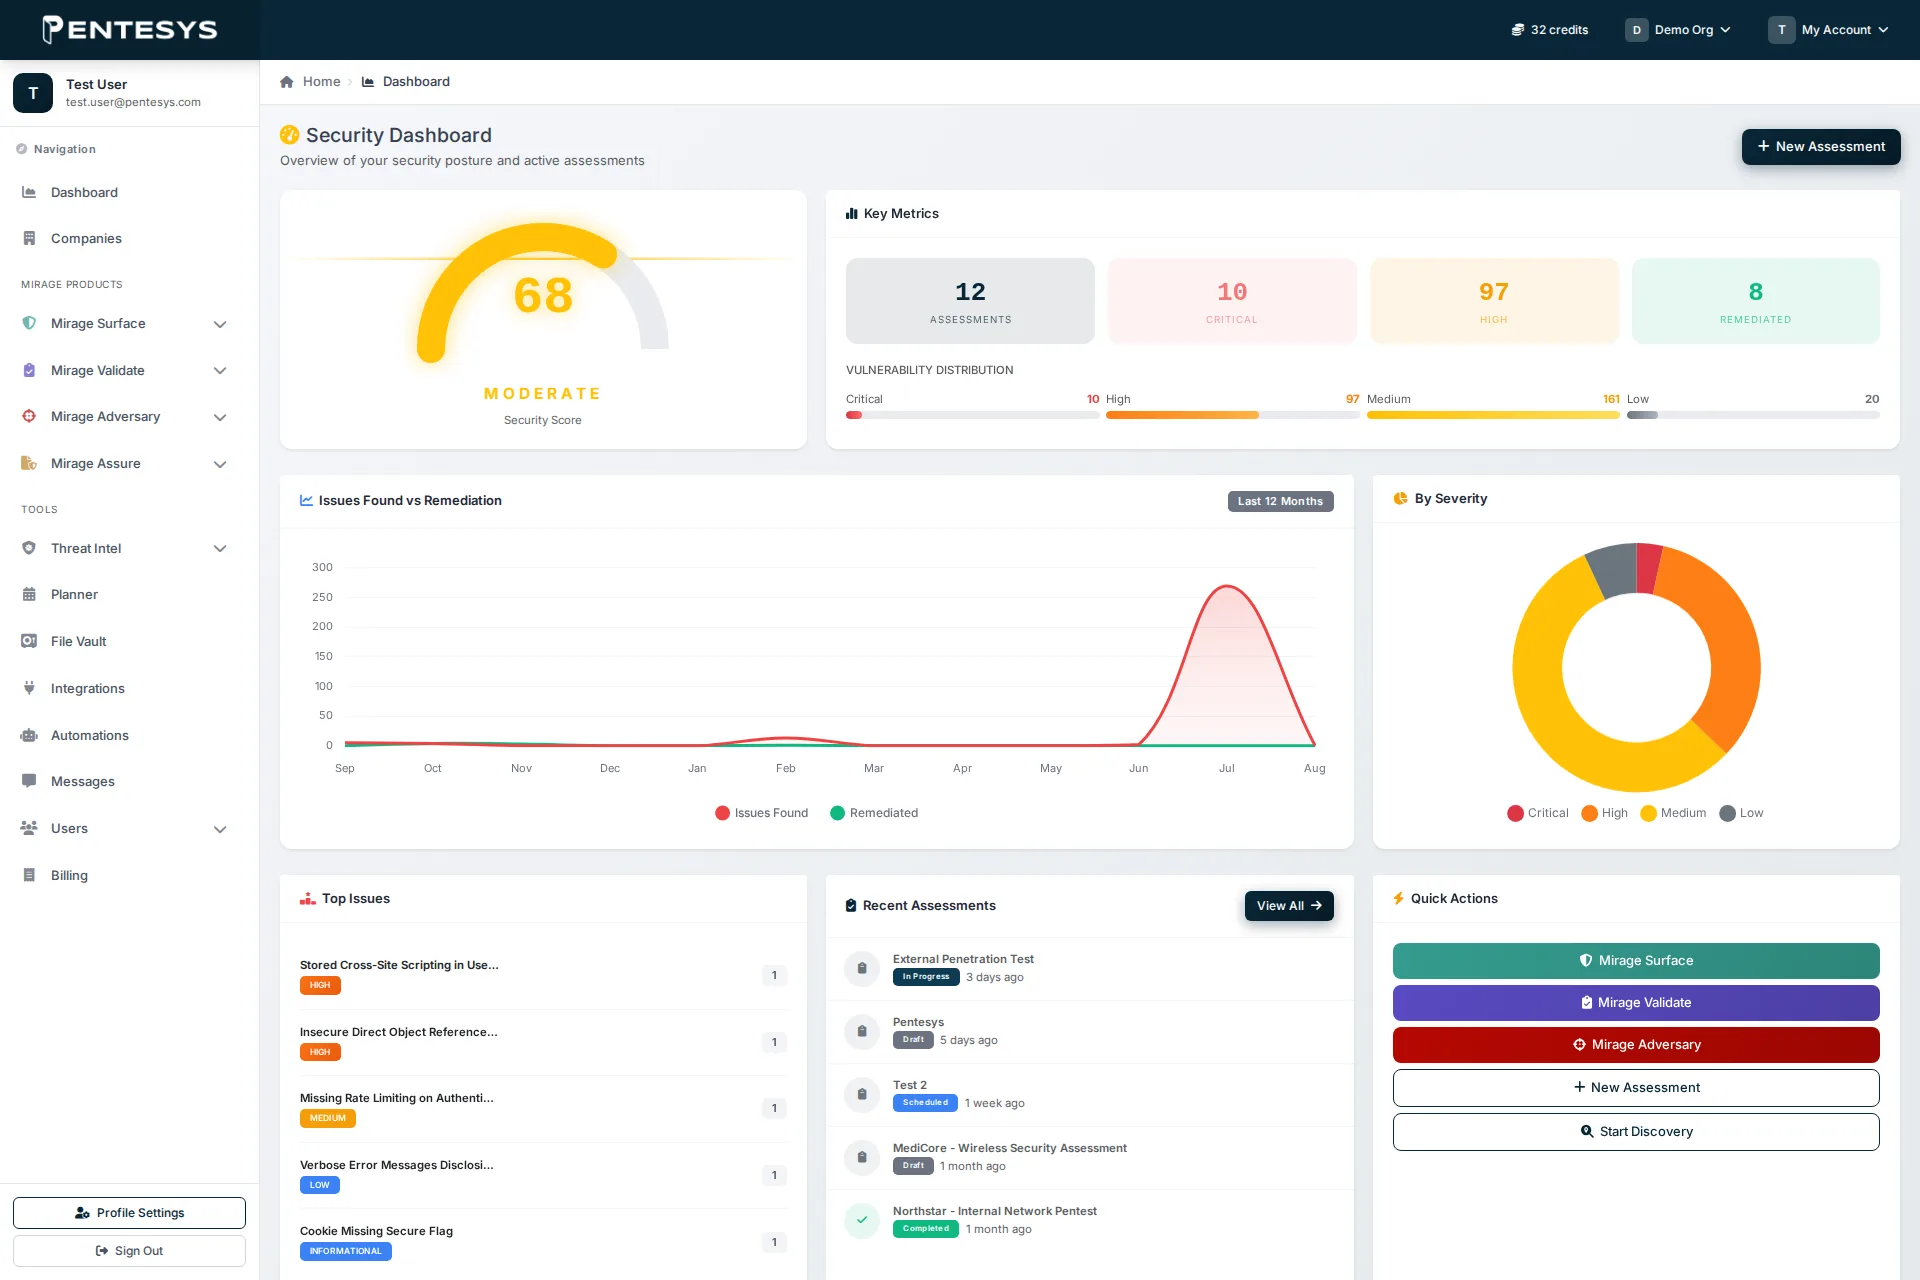
Mirage is the platform behind continuous security at Pentesys — visibility, validation, adversary simulation and assurance in one place.

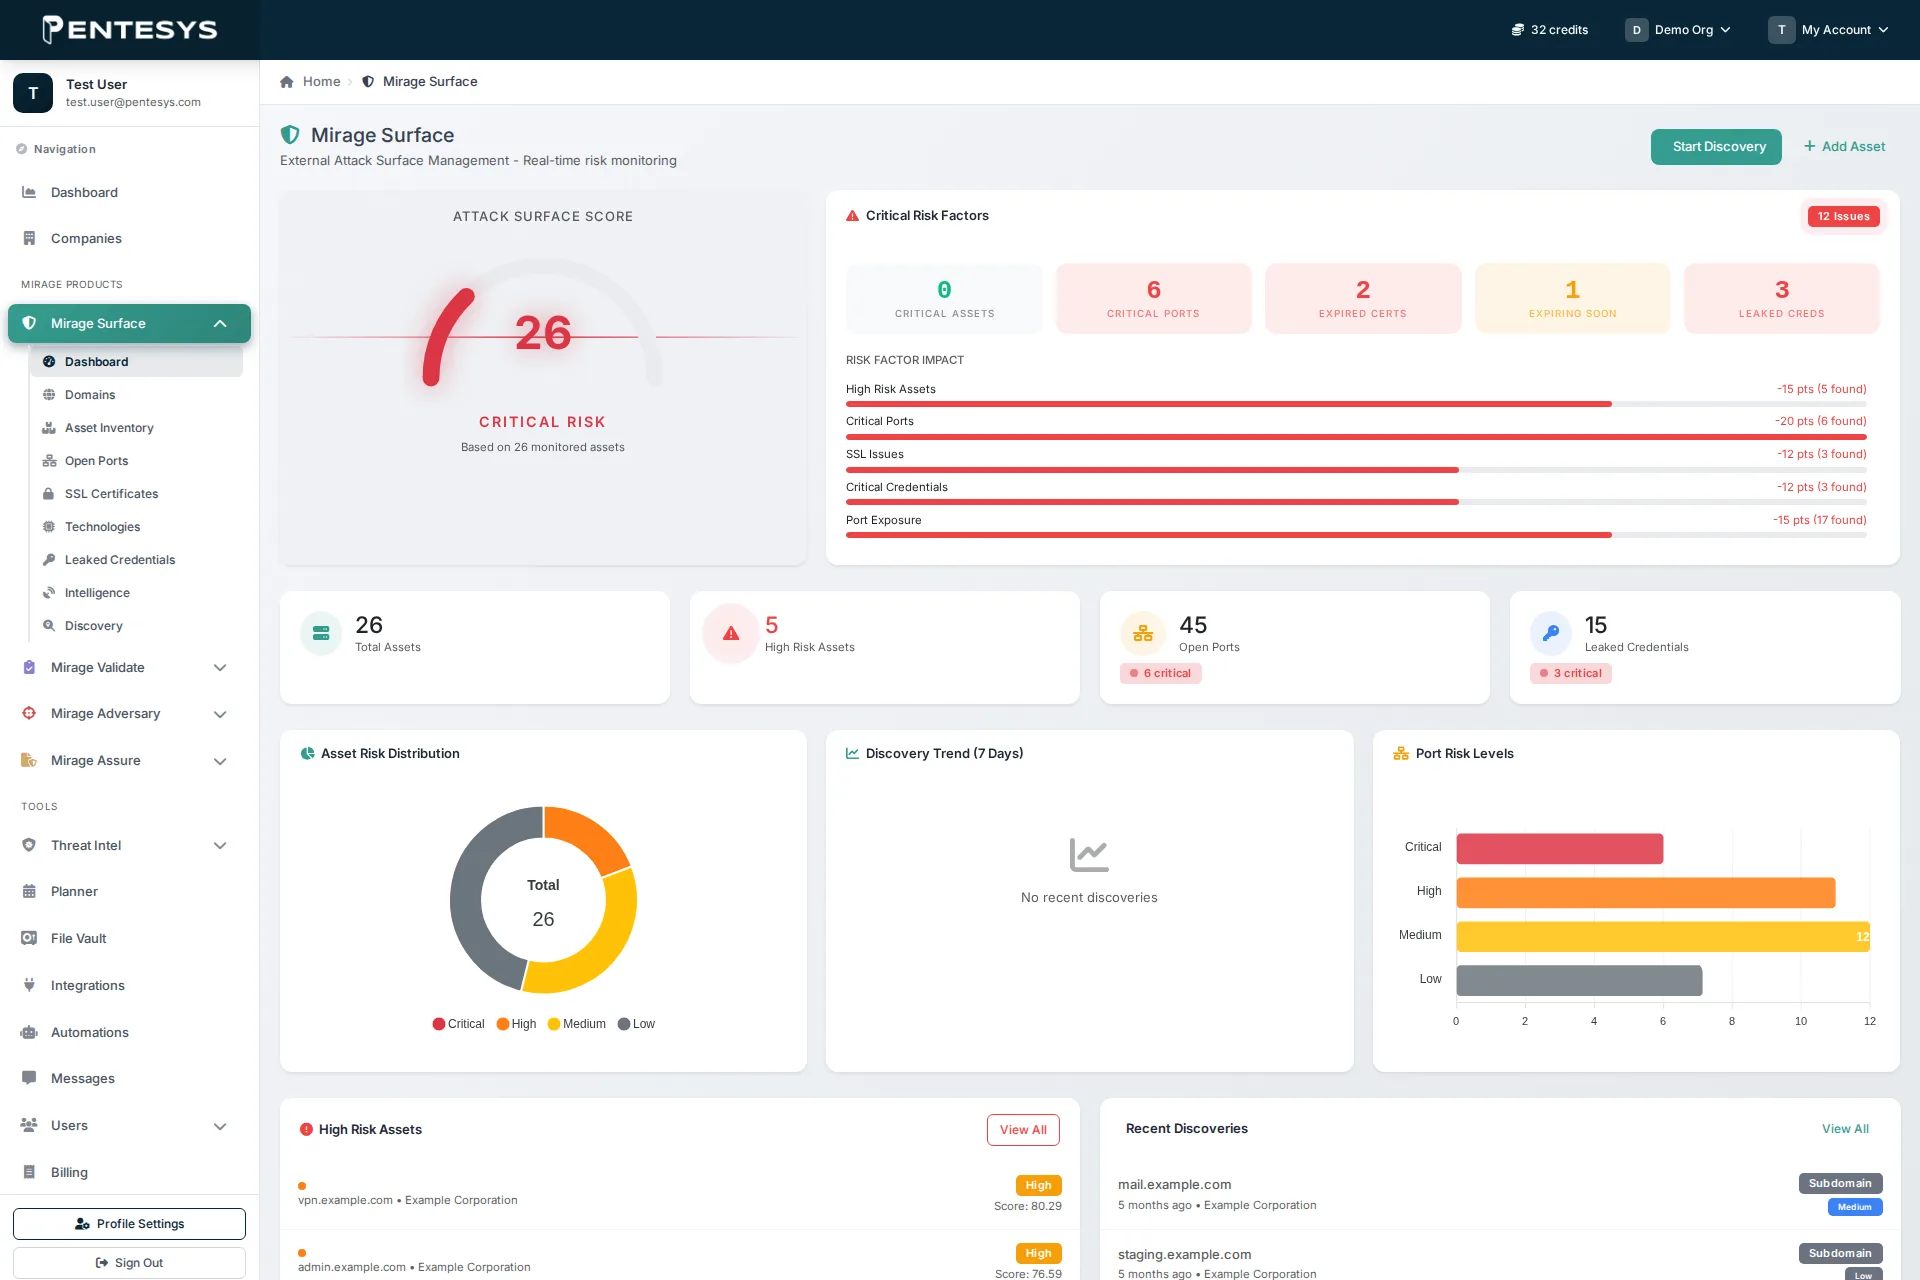
Discover what attackers can see.
External attack surface management and continuous asset discovery.
Learn more
Find and validate vulnerabilities.
Human and AI-assisted penetration testing with findings, remediation and retesting.
Learn more
Test your ability to detect real attacks.
Red teaming and adversary simulation.
Learn more
Prove security and compliance.
Security assurance, governance and Cyber Essentials capabilities.
Learn moreFour routes into Pentesys — pick the one that matches the problem in front of you today.
Web, API, mobile, infrastructure, cloud and application testing.
Scope a Penetration TestContinuous Threat Exposure Management (CTEM): attack-surface discovery, validation and remediation.
Explore Continuous SecurityReal-world adversary simulation designed to test people, process and technology.
Explore Red TeamingCyber Essentials, Cyber Essentials Plus and preparation support.
Explore Cyber EssentialsWe use AI to increase testing speed, coverage and scale across applicable services. Experienced security consultants validate findings, remove false positives and add expert analysis before results reach your team.
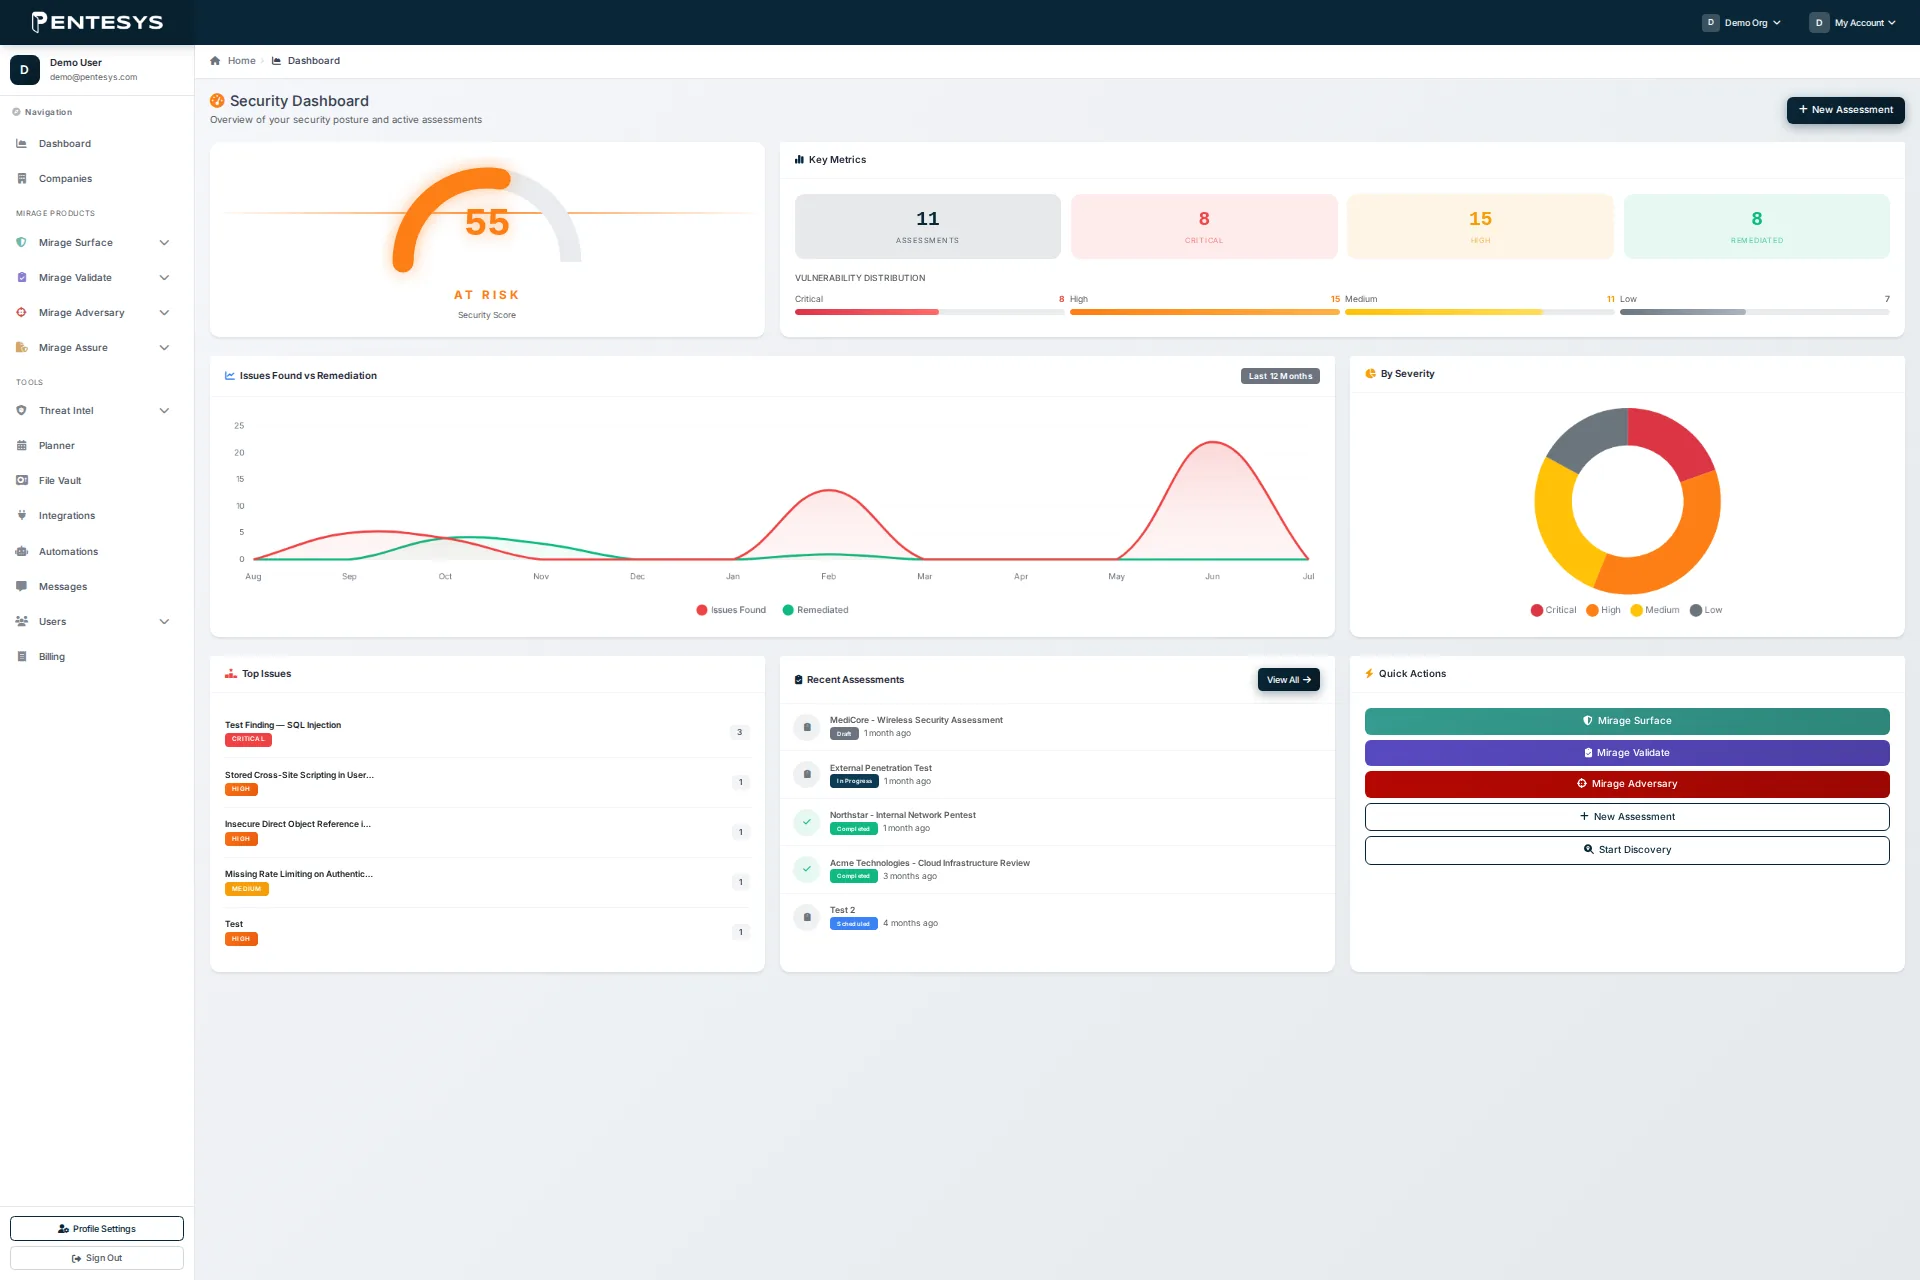
Manage security testing from initial scope through remediation and retesting in the Pentesys portal. Track findings, assets, testing activity and security progress in one place.
Independently assessed methodologies, qualified consultants and reporting suitable for enterprise security, procurement and compliance teams.
Buy a single scoped assessment, a continuous bundle, or a tailored enterprise exposure management programme.
Scoped and fixed-price
For organisations requiring a defined penetration test or security assessment.
Bundles from £4,750
For organisations that require ongoing testing, monitoring and remediation.
Tailored programmes
For larger organisations requiring continuous exposure management, red teaming and assurance.
“Pentesys has continuously performed admirably during our collaboration, giving us faith in their knowledge. They delivered work that above our expectations by approaching each project with a deep understanding of our specifications. Their team demonstrated a remarkable degree of proficiency by effectively pinpointing weaknesses and offering practical suggestions to reduce possible hazards.”
Visit our stand at ExCeL London, 22–24 September 2026, to see the Mirage Portal in action and discuss continuous security testing, red teaming and compliance with the team.
Dates
22 – 24 September 2026
Location
ExCeL London, UK
Stand
To be confirmed
Reserve a 20-minute slot and we will bring a tailored Mirage Portal demo and answer questions about continuous testing, pricing and compliance.
Tell us what you’re trying to protect and we’ll help you choose the right testing approach. Build an indicative scope online or speak directly with our team.
Build an initial scope online with no commitment.
Guidance on continuous security testing, CTEM, EASM and compliance from the Pentesys team.
A balanced, technically grounded comparison of AI-assisted and human-led penetration testing: what each does well, where AI fails, what CREST expects, and how to evaluate an AI-enabled testing provider.
Read article
Pentesys has signed the CREST AI Charter, reinforcing our commitment to the responsible, transparent and professionally governed use of artificial intelligence in cybersecurity.
Read article
An impartial buyer's guide to modern Penetration Testing as a Service platforms, comparing human testing models, portals, continuous testing, integrations and UK delivery.
Read articleWe respond within 24 hours. Tell us what you need to test and we'll shape a programme around it.