
Overview
Penetration testing means different things depending on who is selling it. At one end it is a scanner run against your estate with the output reformatted. At the other it is a consultant spending a fortnight trying to break specific things, with everything they find validated by hand before it reaches you. The price difference between the two is often smaller than the difference in what you get.
This covers what the work involves, how to scope it, what a usable report looks like, and the point at which a single annual test stops being enough. It assumes you are commissioning testing rather than carrying it out.
Defining Pen Testing for the Modern Enterprise
At its core, pen testing is an authorised adversarial simulation designed to evaluate the security of an IT infrastructure. It’s an active attempt to bypass security controls and gain access to systems or data. While many organisations rely on automated tools, a true penetration test is human-led. It requires a specialist to think like an attacker, using creativity and technical skill to find paths that software often misses. You can find a comprehensive overview of penetration testing that details the various methodologies used to secure digital assets.
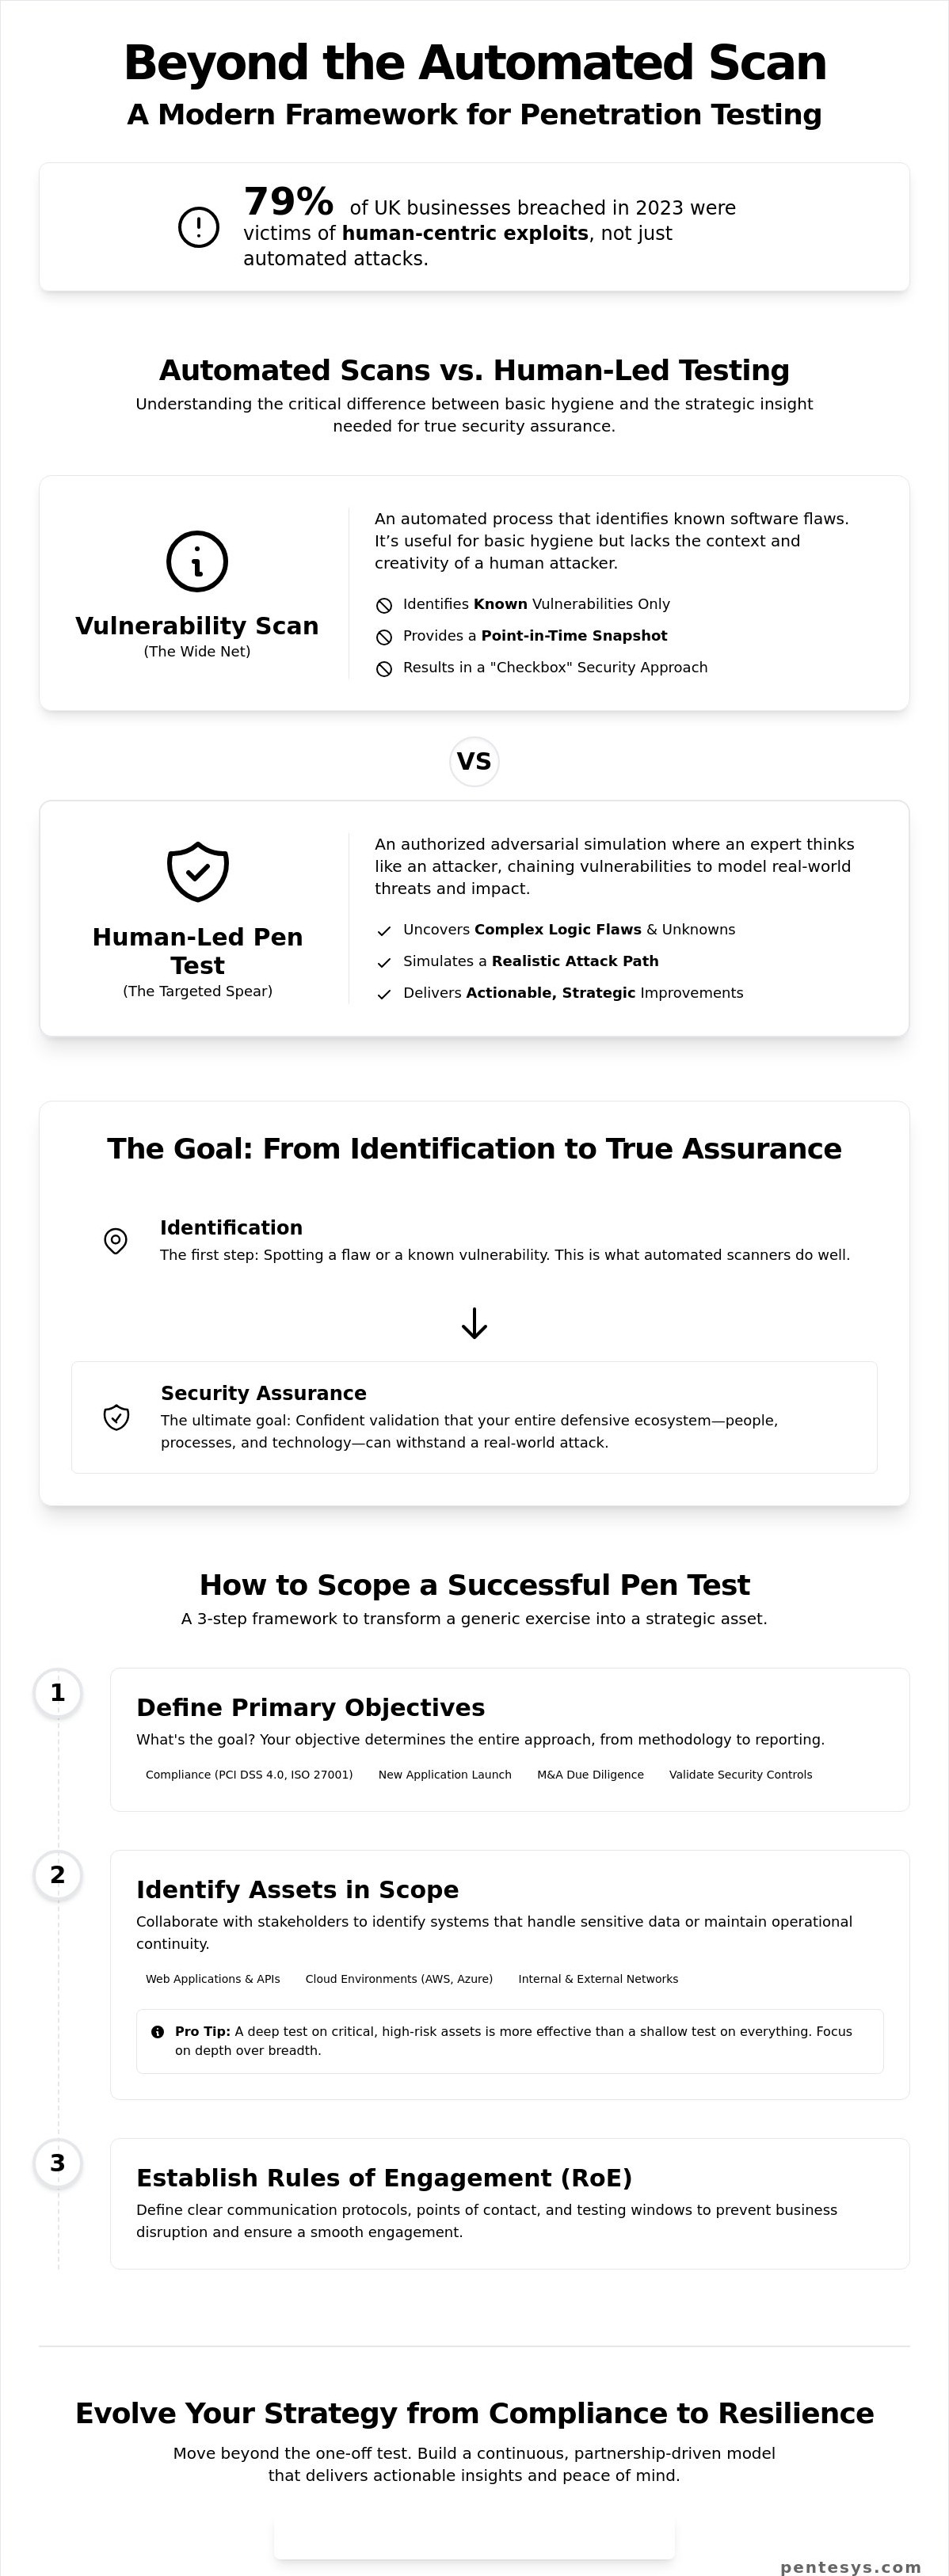
The distinction between a simple vulnerability scan and an expert-led test is critical. Scans are automated processes that identify known software flaws. They’re useful for basic hygiene but they lack context. An expert-led test goes deeper, chaining multiple low-level vulnerabilities together to achieve a high-impact breach. This methodology provides a realistic view of risk that automated tools cannot replicate. The National Cyber Security Centre (NCSC) often compares this process to a financial audit. Just as a financial audit provides independent verification of a company’s accounts, a penetration test provides an independent, technical verification of a company’s security posture.
Assurance vs. Identification: Why the Distinction Matters
Knowing a vulnerability exists is only half the battle. Identification is the act of spotting a flaw; assurance is the process of proving that your entire defensive ecosystem can withstand an attack. Many businesses find that while they’ve identified a bug, their internal remediation and patching processes fail to fix it correctly. A penetration test validates these internal workflows. Security Assurance is the confident validation of defensive measures.
For UK enterprises, this distinction is the difference between a “tick-box” compliance exercise and genuine resilience. Cyber insurance providers now frequently demand evidence of regular testing before offering coverage. By moving beyond simple identification, organisations build long-term trust with stakeholders and regulators alike. This strategic approach ensures that security is a managed, ongoing process rather than a series of disconnected reactions to threats.
How to Scope a Penetration Test: A Step-by-Step Framework
Effective scoping is the foundation of a successful security engagement. It transforms a generic exercise into a strategic asset that provides genuine assurance. Without a clear scope, testing teams may waste hours on low-priority assets while missing critical vulnerabilities in your core infrastructure. The NIST definition of pen testing emphasises the importance of mimicking real-world attack patterns to identify security gaps, and this requires a precise understanding of your environment.
Your first step involves defining the primary objective. An organisation seeking compliance with PCI DSS 4.0, which became mandatory in March 2024, will have different requirements than a startup launching a new fintech application. Once you establish the goal, you must identify the assets in scope. This includes web applications, APIs, cloud environments, and internal networks. Clear communication protocols and a defined testing window are essential to prevent business disruption; testing production environments during peak UK business hours requires careful coordination and established Rules of Engagement (RoE).
Defining Your Testing Boundaries
Identifying critical business assets is a collaborative process between security teams and stakeholders. You should focus on systems that handle sensitive data or maintain operational continuity. A common pitfall in scoping is the desire to test every single IP address or sub-domain. This often dilutes the depth of the assessment. It’s more effective to focus on a smaller, high-risk surface area where a breach would be catastrophic.
Managing third-party dependencies is another vital component. If your infrastructure sits on AWS, Azure, or Google Cloud, you must understand the shared responsibility model. While most major providers no longer require formal notification for standard pen testing, specific high-intensity tests may still trigger automated throttling or security alerts. You must also account for third-party APIs; testing these without explicit permission can lead to legal complications. Our team helps you navigate these complexities through the Pentesys Portal, which serves as a central hub for scoping documentation and asset management.
Selecting the Right Level of Information
The amount of information provided to the testing team dictates the efficiency and focus of the engagement. We categorise these into three primary models:
Choosing the right model ensures your budget is spent on high-value analysis rather than basic reconnaissance. This methodical approach to pen testing ensures your security posture remains resilient against evolving threats.
- Black Box: The tester has zero prior knowledge of the target. This simulates an external adversary starting from scratch. It’s excellent for testing your initial detection and response capabilities.
- White Box: The team receives full transparency, including source code and network diagrams. This allows for a deep-dive into internal logic and configurations, identifying flaws that a surface-level scan would miss.
- Grey Box: This is the most common approach for web applications. The tester is granted basic user credentials. It allows the human-led team to bypass the authentication layer and focus their expertise on finding complex vulnerabilities within the application logic.
Beyond the Automated Scan
Automated scanners struggle with nuanced flaws. For instance, a scanner cannot easily detect a broken access control vulnerability where a user can view another person’s private data by simply changing a digit in a URL. Human testers identify these logic flaws by understanding how an application is intended to function. Manual verification is essential to eliminate the false positives that often clutter automated reports, saving your internal teams from chasing non-existent threats. Our experts think like an adversary, attempting to bypass modern security controls using creative, multi-stage attack paths that signature-based tools simply cannot replicate. This process provides the peace of mind that your defences have been tested against genuine human ingenuity.
Offensive Security Standards and Frameworks
We align our methodology with globally recognised benchmarks to provide measurable assurance. Our teams prioritise the OWASP Top 10, focusing on critical risks such as Broken Access Control and Cryptographic Failures which accounted for a significant portion of web vulnerabilities in 2023. To provide a realistic view of risk, we map our findings to the MITRE ATT&CK framework. This allows us to simulate the specific tactics, techniques, and procedures used by real-world threat actors. In the UK security market, technical authority is non-negotiable. This is why Pentesys maintains CREST accreditation. This certification guarantees that our pen testing professionals possess the verified skills and ethical standards required to handle sensitive infrastructure. It transforms a simple technical check into a robust strategic asset that supports long-term business resilience.
By moving beyond static scans, we offer a partnership that prioritises quality over speed. Our methodology ensures that every finding delivered through the Pentesys Portal is actionable and accurate. This level of rigour is what separates a routine compliance exercise from a true security assurance programme. We focus on providing the clarity you need to make informed, risk-based decisions for your organisation’s future.
Interpreting the Final Report
A sophisticated report balances an executive summary with a technical deep-dive. The summary provides a high-level view of the security posture for stakeholders, while the deep-dive offers the granular detail developers need to reproduce and fix issues. You’ll encounter risk ratings based on the Common Vulnerability Scoring System (CVSS), but these scores require context. A “High” rating on an internal system with no sensitive data might be less critical than a “Medium” vulnerability on a public-facing UK GDPR-regulated database. A report is a roadmap for resilience, not a list of failures.
A high-standard report should always include:
The Pentesys Portal acts as the central hub for managing this data. By moving away from static documents, the portal provides a dynamic environment where you can track vulnerabilities from identification to resolution in real-time. This proprietary technology ensures that your security posture is visible and manageable at all times, making the transition from “vulnerable” to “assured” a transparent and measurable process.
- Detailed Proof of Concept: Step-by-step evidence showing exactly how a vulnerability was identified and exploited.
- Business Impact Analysis: An assessment of what a successful breach would cost the business in terms of downtime, reputation, or regulatory fines.
- Remediation Guidance: Clear, actionable instructions that allow IT teams to implement technical fixes without guesswork.
The Remediation Cycle
Remediation is a collaborative effort. Security experts work alongside your developers to ensure that fixes are robust and don’t introduce new issues. This partnership is vital because many incidents stem from known vulnerabilities that lacked a clear fix plan. Following the implementation of patches, re-testing is a non-negotiable step to confirm that the security gaps are successfully closed. This cycle doesn’t just fix immediate problems; it provides the data needed to inform long-term strategic security investments. Using pen testing data allows you to move from reactive patching to a proactive, enterprise-grade security strategy.
Beyond the One-Off Test: Building a Continuous Assurance Strategy
An annual test describes your estate on the day it was tested. Anything deployed since is untested. For teams shipping weekly that means the report is partly out of date before it has been read, and the gap widens for the eleven months until the next one.
Two things narrow that gap. Continuous penetration testing spreads consultant time across the year rather than concentrating it in one block. Continuous threat exposure management puts a loop around the whole thing: discover what is exposed, validate what is genuinely exploitable, fix it, then prove the fix held. Neither removes the need for deep manual testing on the systems that matter most.
- Real-time visibility: Identify new assets and misconfigurations within hours of deployment.
- Reduced window of risk: Close the gap between vulnerability discovery and remediation.
- Agile alignment: Synchronise security testing with your development sprints and release cycles.
Web Application and API Penetration Testing
Web applications often serve as the primary gateway for sensitive customer data. Our human-led assessments focus on the OWASP Top 10, identifying critical flaws like Broken Access Control and Injection. APIs represent the new frontier for data breaches in the UK, with the Verizon Data Breach Investigations Report highlighting that web application attacks are involved in a significant share of all breaches. We test both authenticated and unauthenticated states to ensure that logic flaws in SaaS platforms do not permit unauthorised data extraction. This rigorous process ensures that your bespoke software remains a business asset rather than a liability.
Infrastructure and Network Assessments
Network security requires a dual perspective to be effective. External testing simulates an attacker attempting to breach the perimeter, while internal testing addresses the “insider threat” or the potential for lateral movement following a successful initial compromise. Many UK enterprises still operate legacy systems that lack modern security patches. We prioritise hardening network configurations and identifying these legacy weaknesses. Our methodology includes detailed audits of firewall configurations and network segmentation, ensuring that a single compromised device cannot lead to a full-scale estate breach.
Cloud Security and Adversarial Simulations
Cloud environments such as AWS, Azure, and GCP introduce complex Identity and Access Management (IAM) challenges. Misconfigurations in these settings are a leading cause of data exposure, often occurring when permissions are overly permissive. While standard penetration testing identifies technical gaps, our advanced Red Teaming goes further by simulating a persistent adversary. This includes testing the human element through sophisticated social engineering and phishing simulations. By mimicking real-world attack patterns, we provide actionable insights that help your team build long-term resilience against evolving threats. All findings are delivered through the Pentesys Portal, providing a central hub for remediation guidance and strategic security management.
How long does a typical penetration test take to complete?
A typical engagement takes between 5 and 15 working days to complete, depending on the scope of your infrastructure. Smaller web applications might require only 3 days of active testing, whereas complex enterprise networks often demand 10 days or more. We provide a clear timeline during the planning phase, ensuring you receive detailed reports through the Pentesys Portal within 48 hours of the testing conclusion.
Will a penetration test cause downtime for my business?
Professional pen testing is designed to be non-disruptive and shouldn’t cause downtime for your business operations. Our consultants work within agreed parameters and use controlled exploitation techniques to maintain system stability. We coordinate closely with your technical team to schedule intensive tests during low-traffic periods, protecting uptime while we identify security gaps across your estate.
How often should my organisation perform a pen test?
You should perform a pen test at least once every 12 months or whenever you implement major infrastructure changes. The CREST guidelines recommend this annual frequency to maintain a strong security posture. Organisations handling sensitive data often increase this to quarterly assessments to address the 22,000 new vulnerabilities discovered annually across the global threat landscape, ensuring continuous resilience against emerging risks.
What is the difference between red teaming and pen testing?
Pen testing focuses on identifying and exploiting as many vulnerabilities as possible within a specific scope, while red teaming is an adversary simulation designed to test your organisation’s detection and response capabilities. Red team engagements are often unannounced and multi-layered, typically lasting for 4 to 8 weeks. This strategic approach provides a holistic view of how your security team reacts to a real-world, persistent threat.
What information do I need to provide for an accurate quote?
To provide an accurate quote, we require the number of internal and external IP addresses, the count of web application pages, and any specific compliance goals. You’ll also need to specify if the test is “black box” or “white box” to help us determine the required consultant hours. This data allows us to build a transparent proposal that reflects the exact technical requirements of your UK-based infrastructure.
Founder & CEO, Pentesys
James Hinton is the founder of Pentesys, a CREST-approved UK company working only on offensive security: penetration testing, PTaaS, CTEM, external attack surface management and red teaming. He built the business around one discipline rather than a broad consultancy menu, and most of his time still goes on how engagements get scoped, delivered and reported. He writes here about the practical side of security testing and what buyers should be asking for.
LinkedIn profile